Alert List

Check Box:After selecting, click "Export" to export the alert to the local machine as a des3 file; alerts of the official and DSL types do not support export.
Function List: Explained below from left to right.

(1)Edit: Click to enter the alert editing page.
(2)Delete: Click to delete the alert setting.
(3)View: Click to open the event list of the alert, where users can view the events triggered by the alert.

- Name: The alert name, which can be edited on the editing page.
- Description: The alert description, which can be edited on the editing page.
- Level: The alert level, divided into high/medium/low, can be edited on the editing page.
- Enabled: Displayed if the alert is enabled
 ; otherwise, it is shown as disabled
 .
Add Alert
Click the "Add +" icon to open the create alert page.
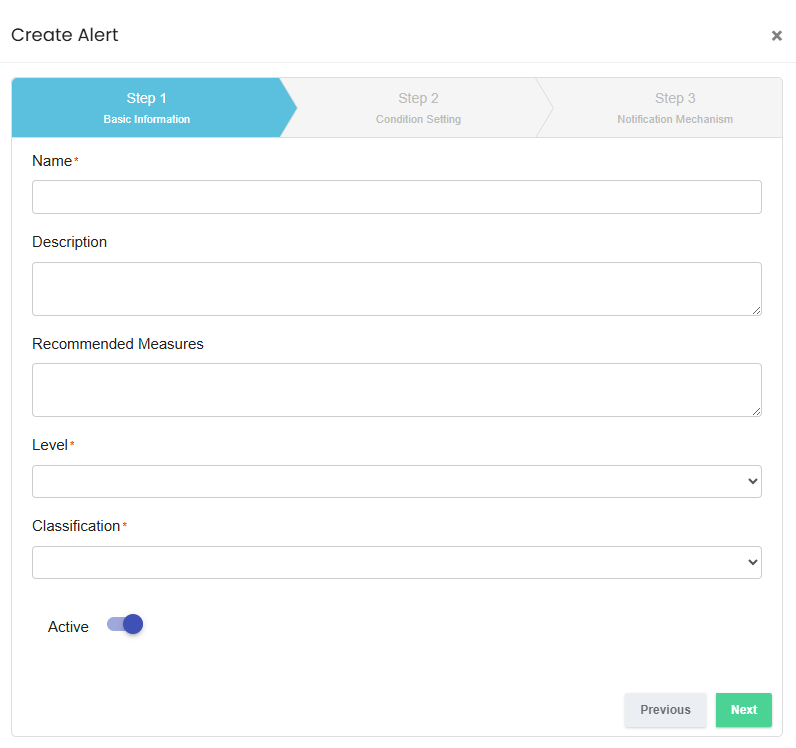
- Name: Required field, up to 128 characters.
- Description: Users can enter content based on their needs, up to 128 characters.
- Recommended Measures: Users can enter content based on their needs.
- Level: Dropdown menu, users can set the level as high/medium/low as needed.
- Category: Dropdown menu, users can set the alert category as security/performance/traffic/other as needed.
- Enable: Click the switch to enable/disable the alert, the new alert is enabled by default.
(1)Condition Settings
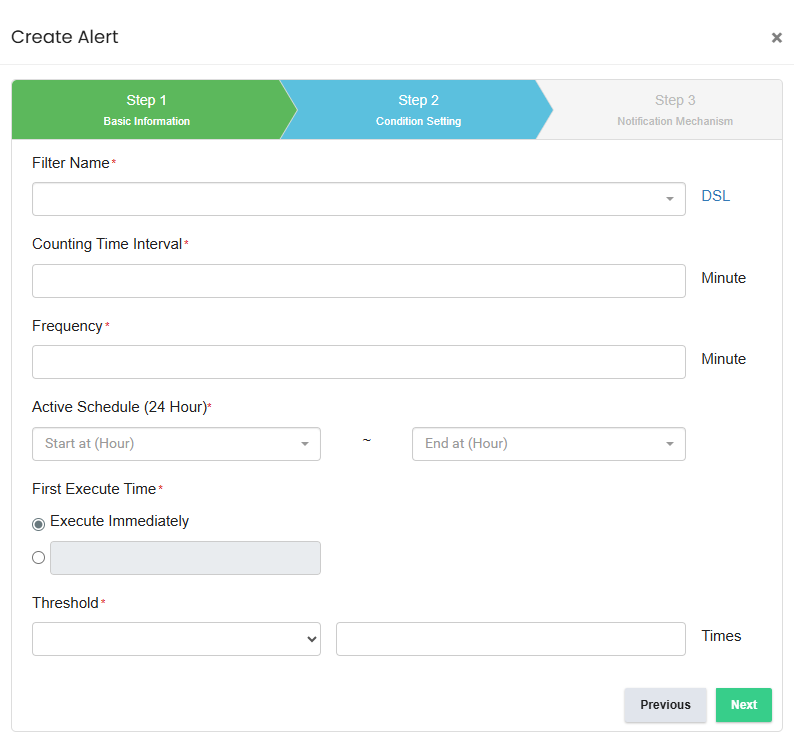
- Filter Condition Name: Dropdown menu to select a saved search condition as the alert filter condition; the input box allows text input for keyword search.
- Support for DQL syntax filter conditions: Click on 'DSL' to open the DSL editing page, allowing administrators to add DQL syntax (JSON). The DSL conditions will be saved in the database and can be selected from the drop-down menu.


2.Trigger Conditions
- Counting time interval: Only numeric input is allowed, used to set the alert filter condition check range.
- Frequency: Only numeric input is allowed, used to set the frequency of alert notifications.
- Active schedule: 24-hour format, a drop-down menu allows selection of the alert notification time interval.
- First Execution Time: There are two options below:
- Immediate Execution: The alert operation will be executed immediately after saving the alert.
- Scheduled Execution Time: Set a specific time when the alert operation will start.
- Threshold: Only numeric input is allowed, used to set the trigger conditions for the alert filter.
3.Notification Mechanism

(1) Email:Check the box to use Email to send alert notifications.
- Recipient Role: Required field, dropdown menu to select system role group.
- Custom Email Subject: Optional field, users can enter parameters as per the instructions on the right to customize the Email subject.
- Display Matching Logs
Latest Log: Attach the last raw log that triggered the condition to the Email.

All Log(Attached File): Dropdown menu to choose an attachment that presents the logs matching the trigger condition in a table.

(2) Export Syslog: Check the box to send the same log to a target IP address when receiving the alert notification.
- Check the Syslog notification box to enable; the fields cannot be filled out if not enabled.
- Enter the IP address and Port to receive the alert (the firewall on the target address must be opened).
(3) InspireOZ: Check the box to enable the InspireOZ automatic ticketing feature.
- Check the IFTTT box to enable the field editing; the fields cannot be filled out if not enabled.
(4) IFTTT: Check the box to enable the IFTTT notification feature.
- Check the IFTTT box to enable the field editing; the fields cannot be filled out if not enabled.
- Enter the notification event name and key (the key setting must be confirmed with the SAFE 3.0 installation and maintenance personnel).

Events
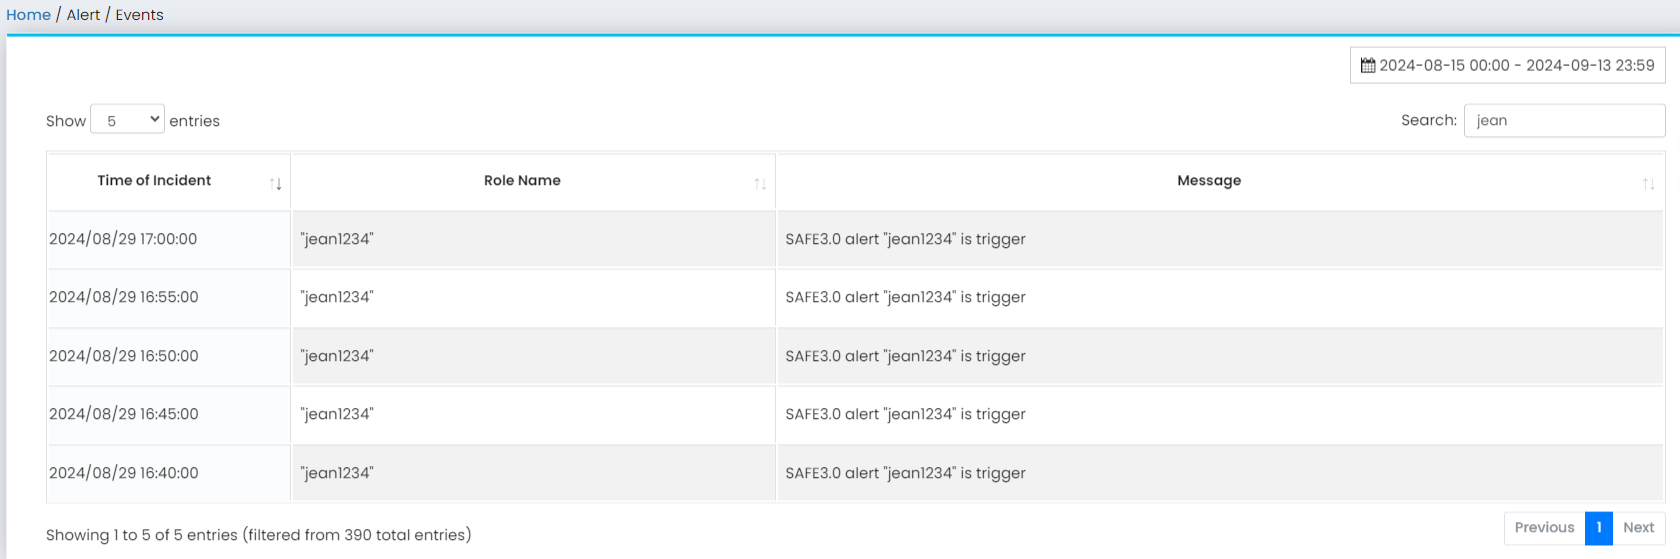
(1) Go to the left list "Alert" → "Events" to enter the alert event list page.
(2) The event list page allows you to view all triggered alert events by incident time, rule name, and message.
(3) Use the sorting icon of the column name to sort according to user needs.
(4) Use the date picker to filter alert event times, or use the search input box for fuzzy keyword search.