Logs
Select "Logs" → "Search" from the left menu to access the basic search page.

1.Field Settings
(1) Click "Field Setting" icon to open the field settings window. Once finished, click "Save" to complete the settings.

(2) Relational Query Field Settings
Click on the blank space in the input box to open the dropdown menu, allowing users to set search fields as needed.
You can set search fields for Destination IP/Destination Port/Source IP/Source Port/Action, and input keywords for success and failure.
(3) Windows Field Settings
Set the search field for the Event ID.
Click on the blank space in the input box to open the dropdown menu for setting the search Event ID.
2. Search Functionality
(1) Relational Search: Directly input Source IP/Destination IP/Source Port/Destination Port information to query specific IP/Port events.

(2) Windows:Directly input the host's hostname or select a preset account audit event from the dropdown menu to search for events.

3. Query Results
- Click the "Export Search" icon to export logs in CSV format.

- Click the "Host Distribution" to open the top5 host list.

- Click the host name or host ip to open the host search result.

Advance Search
1. Search Sources
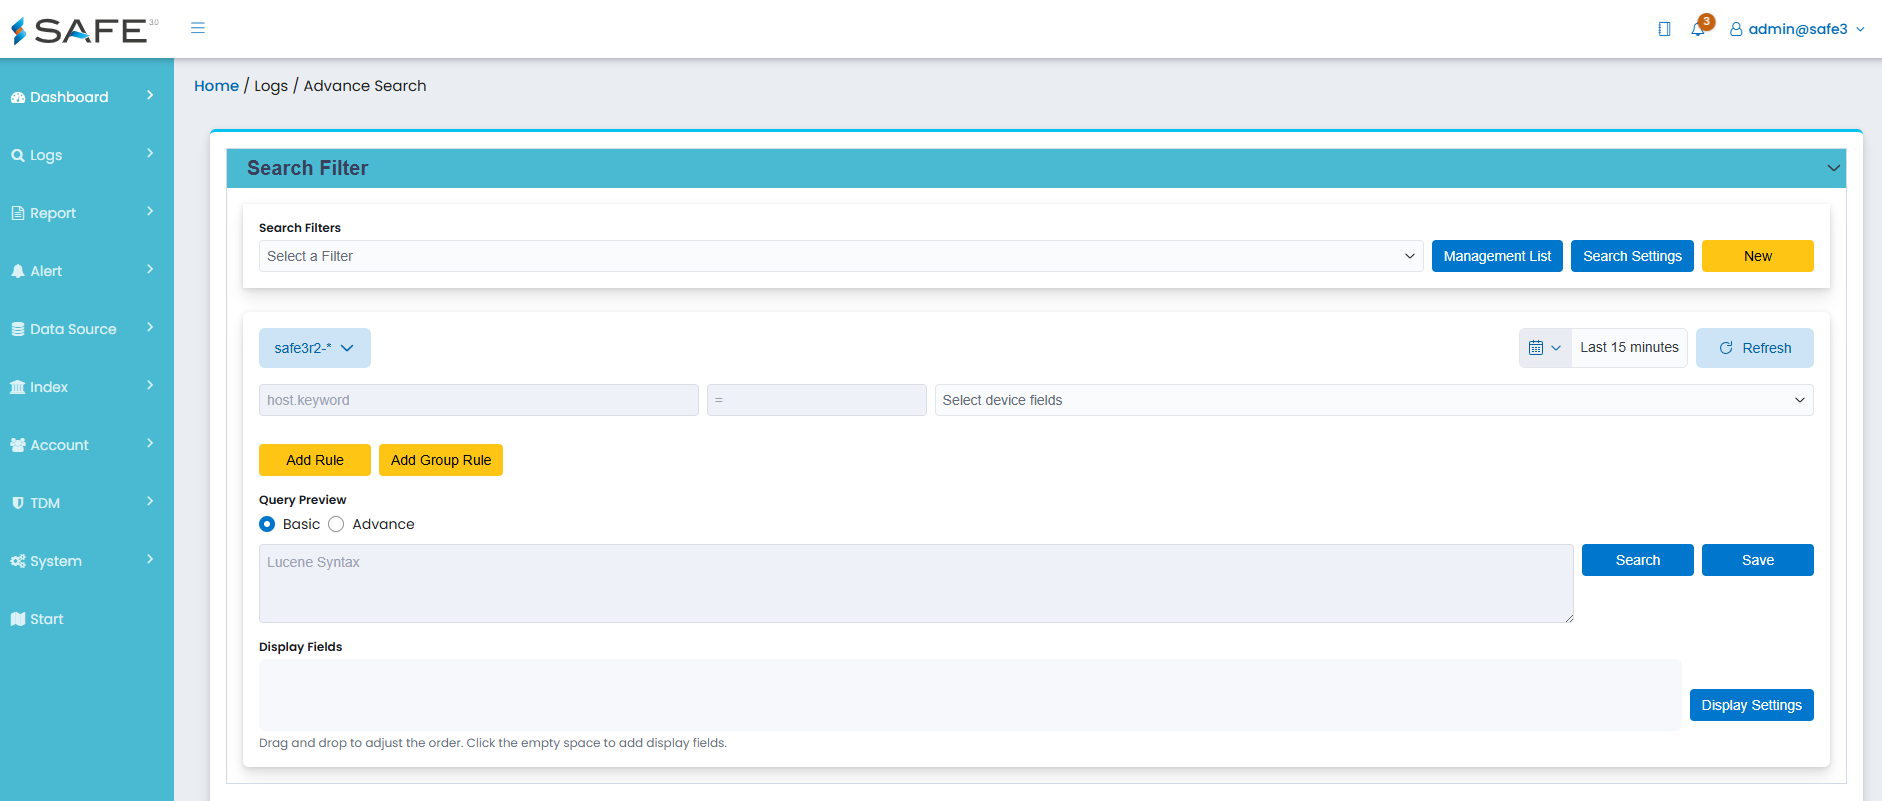
The indices corresponding to various logs are as follows:
(1)metricbeat-*:Represents the host's system monitoring logs.
(2)weblog-*:Represents the Safe3.0 web activity logs.
(3)safe3r2-*:Represents host client logs.
2. Search Filter Feature Introduction
(1) Select Filter Conditions
Users can select predefined filter conditions to apply during log searches.
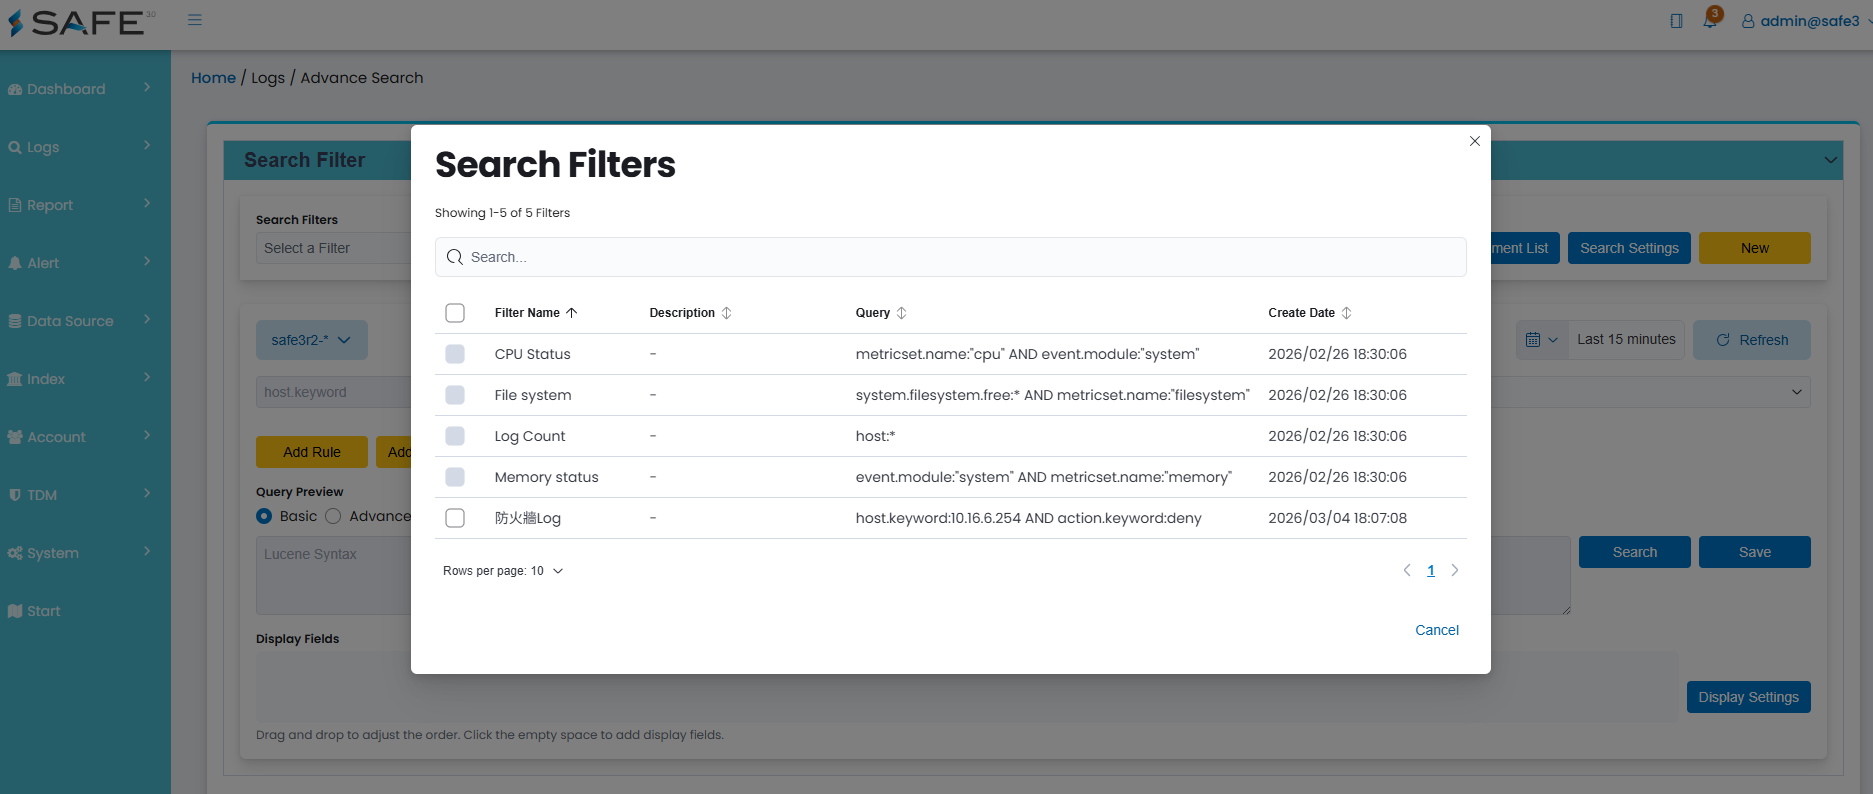
(2) Management List
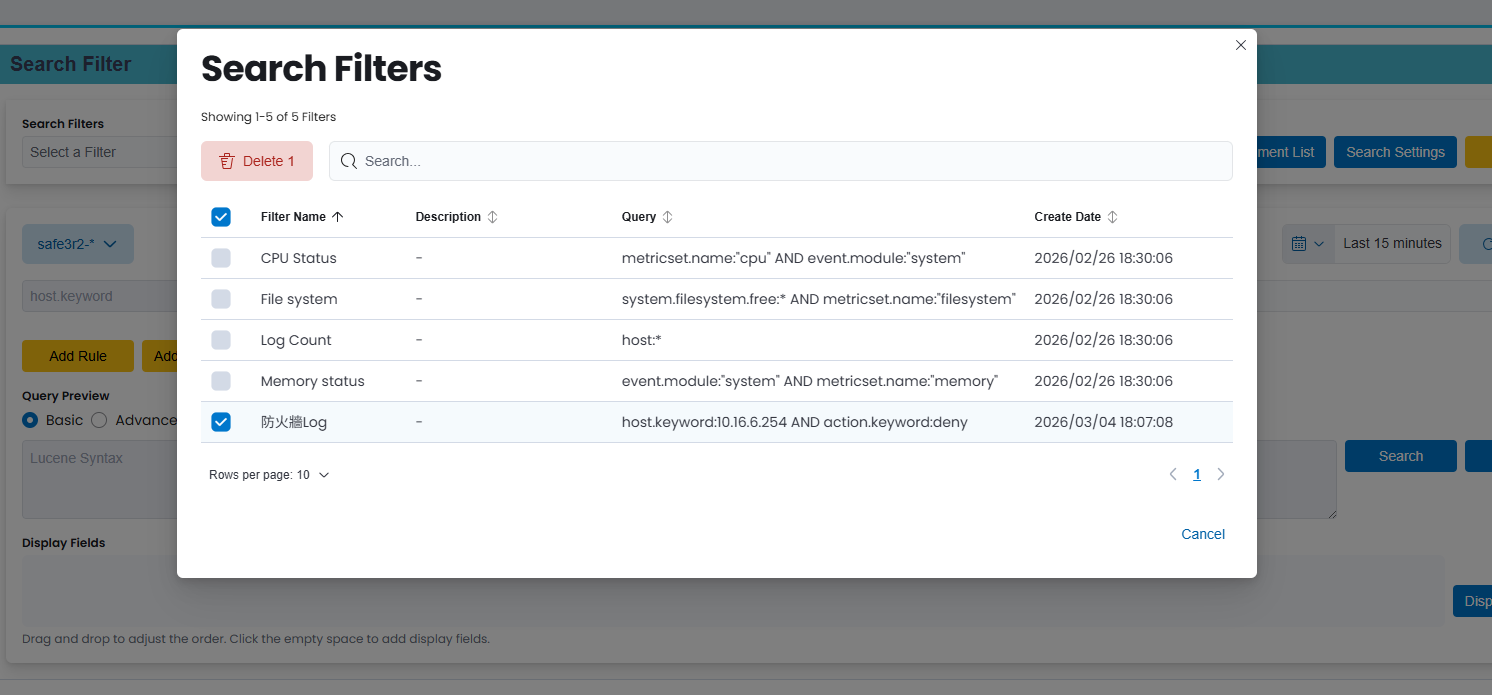
- Click “Management List” to open the rule management window. The system displays the following information in a list format:Filter name / Description / Query / Create date
-
Delete Filter ConditionsDefault filter conditions cannot be deleted, and their checkbox will appear disabled.
-
To delete a filter condition:
-
Select the checkbox of the desired condition.
-
Click the Delete button to remove it.
-
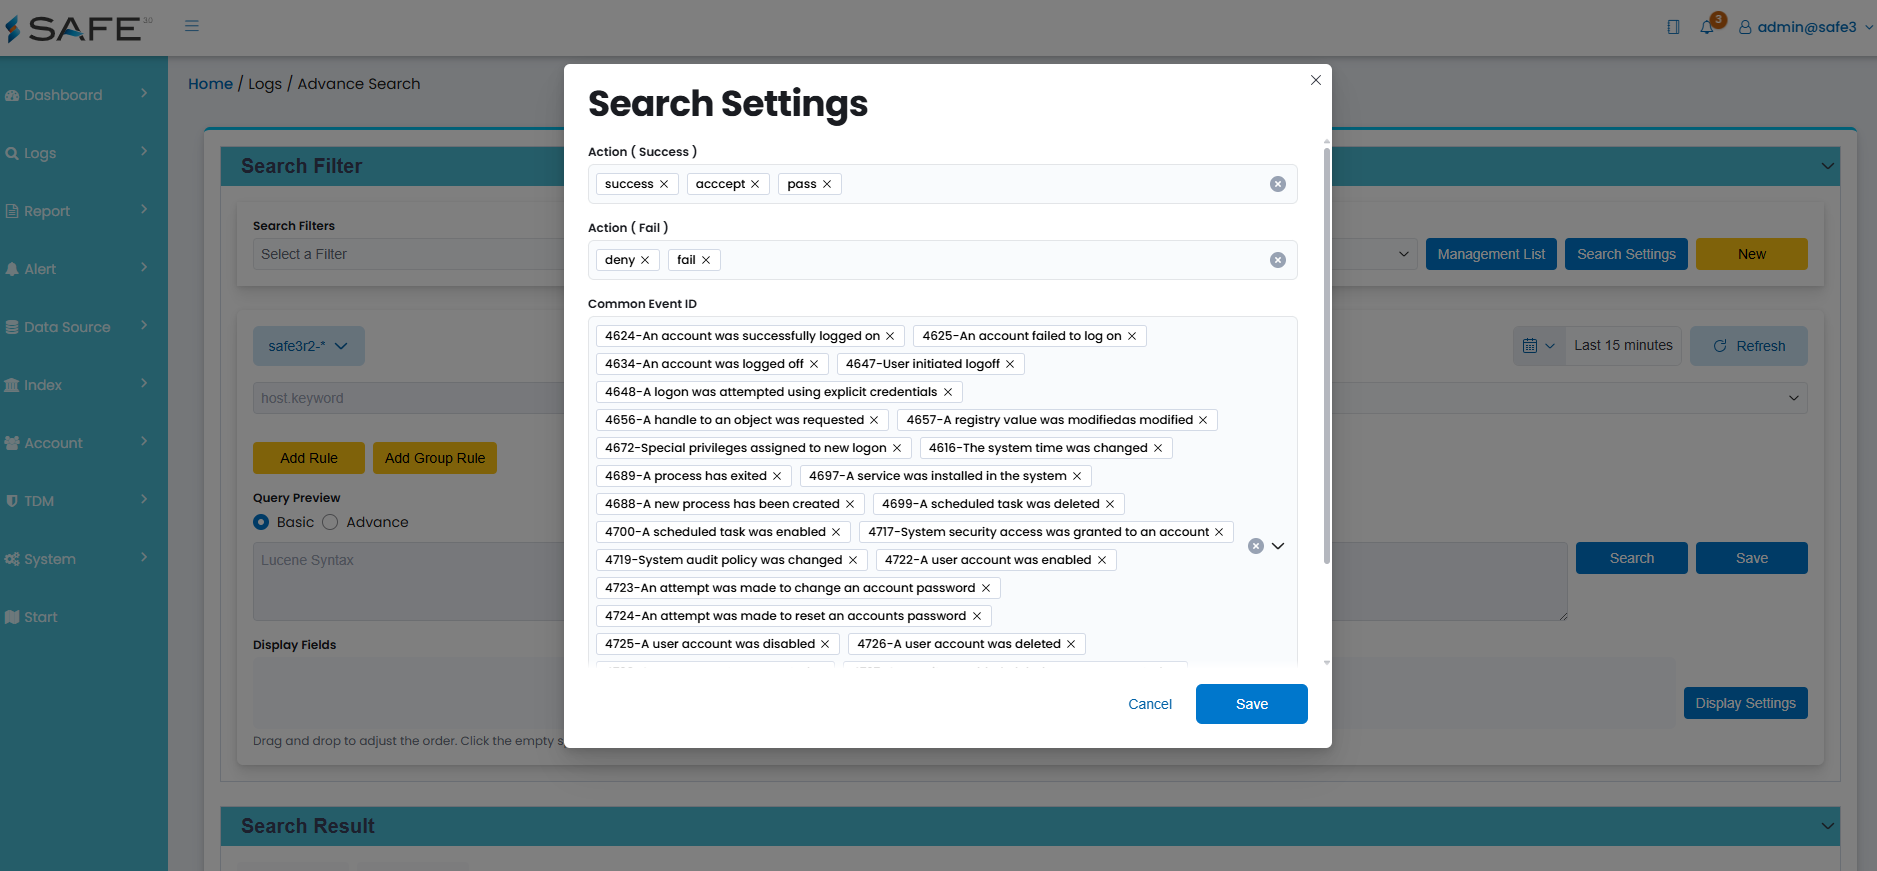
(3) Search Settings
- Users can configure keywords representing successful and failed actions for different device vendors in the default action field.
- Examples:
- Successful actions: accept, success, pass
- Failed actions: deny, fail
-
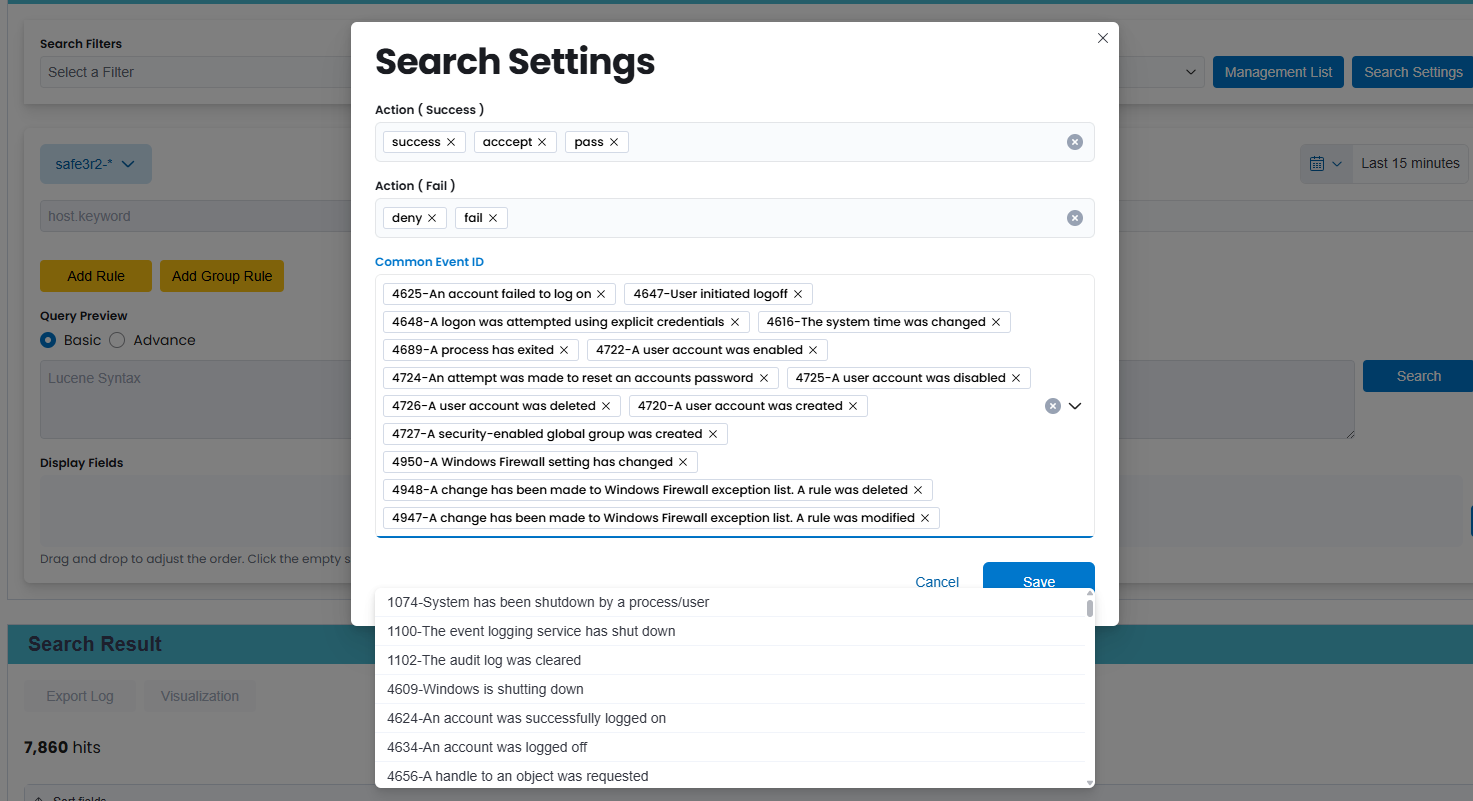
Common Event ID:A dropdown list allows users to select frequently used Windows Event IDs.
- After completing the settings, users can choose the default action field when defining rules and select one of the following options according to their needs:
- All
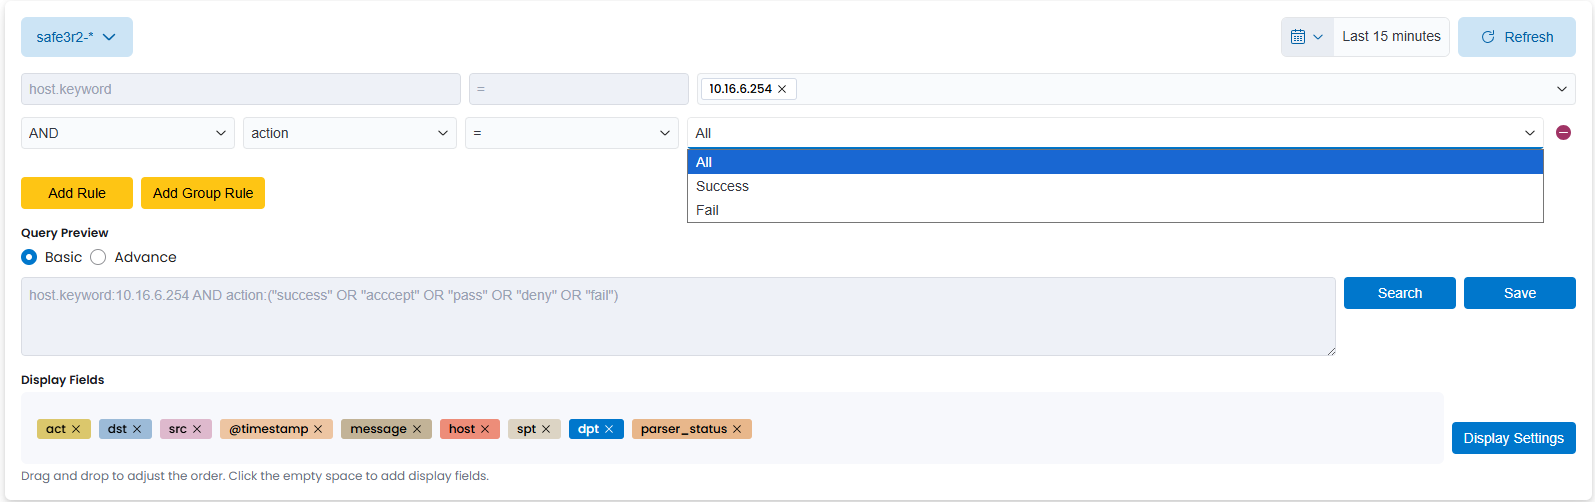
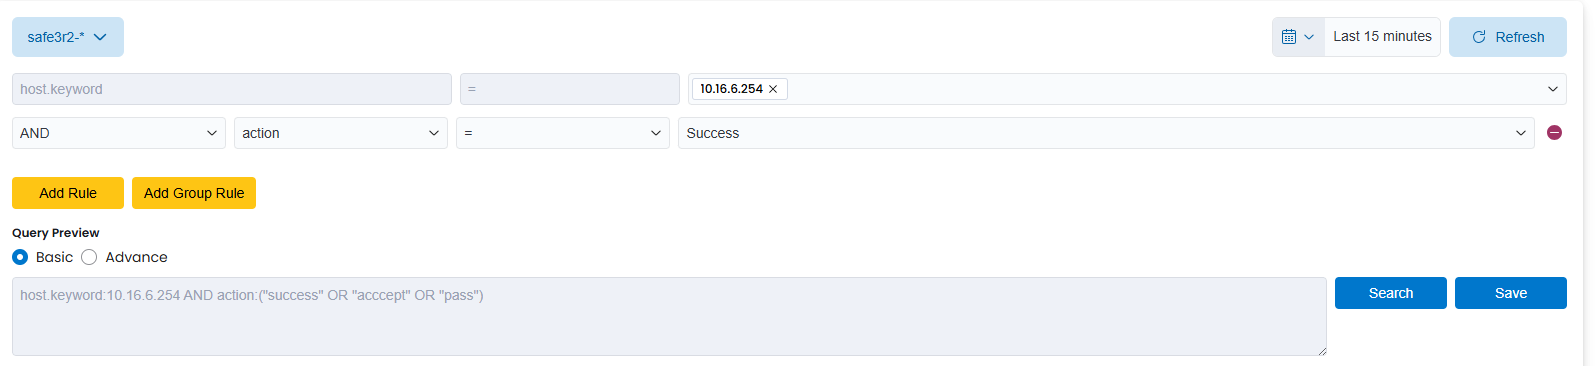
- Success
- Failure
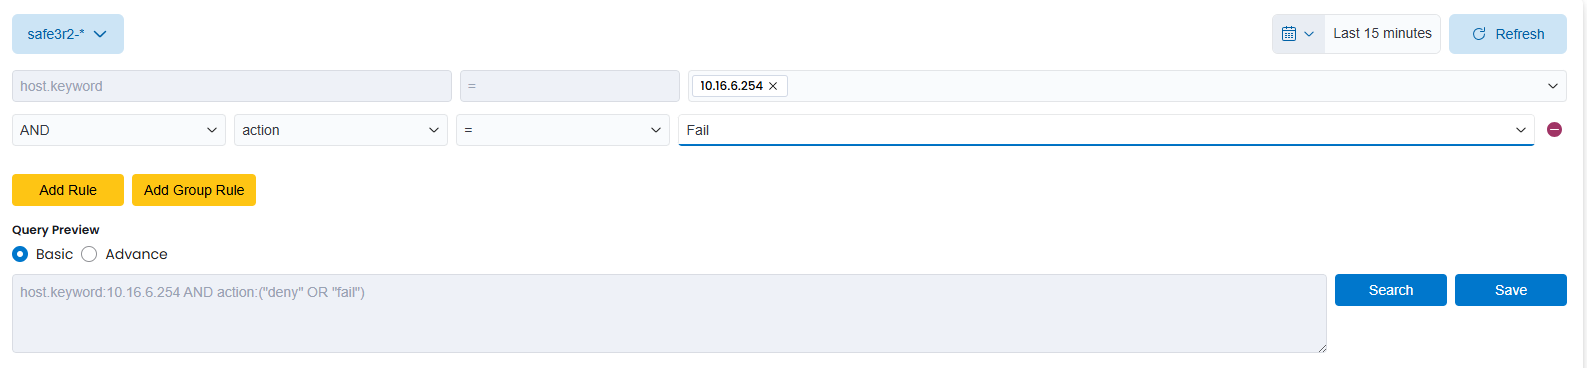
- All conditions within each action category are connected using the OR operator.
- Common Event ID Usage:By selecting the EventID field, the configured Event ID dropdown list will appear.
Each selected event ID is connected using the OR operator.
(4) Add New Rule:Click the “Add” button to clear the existing search settings and create a new search condition.
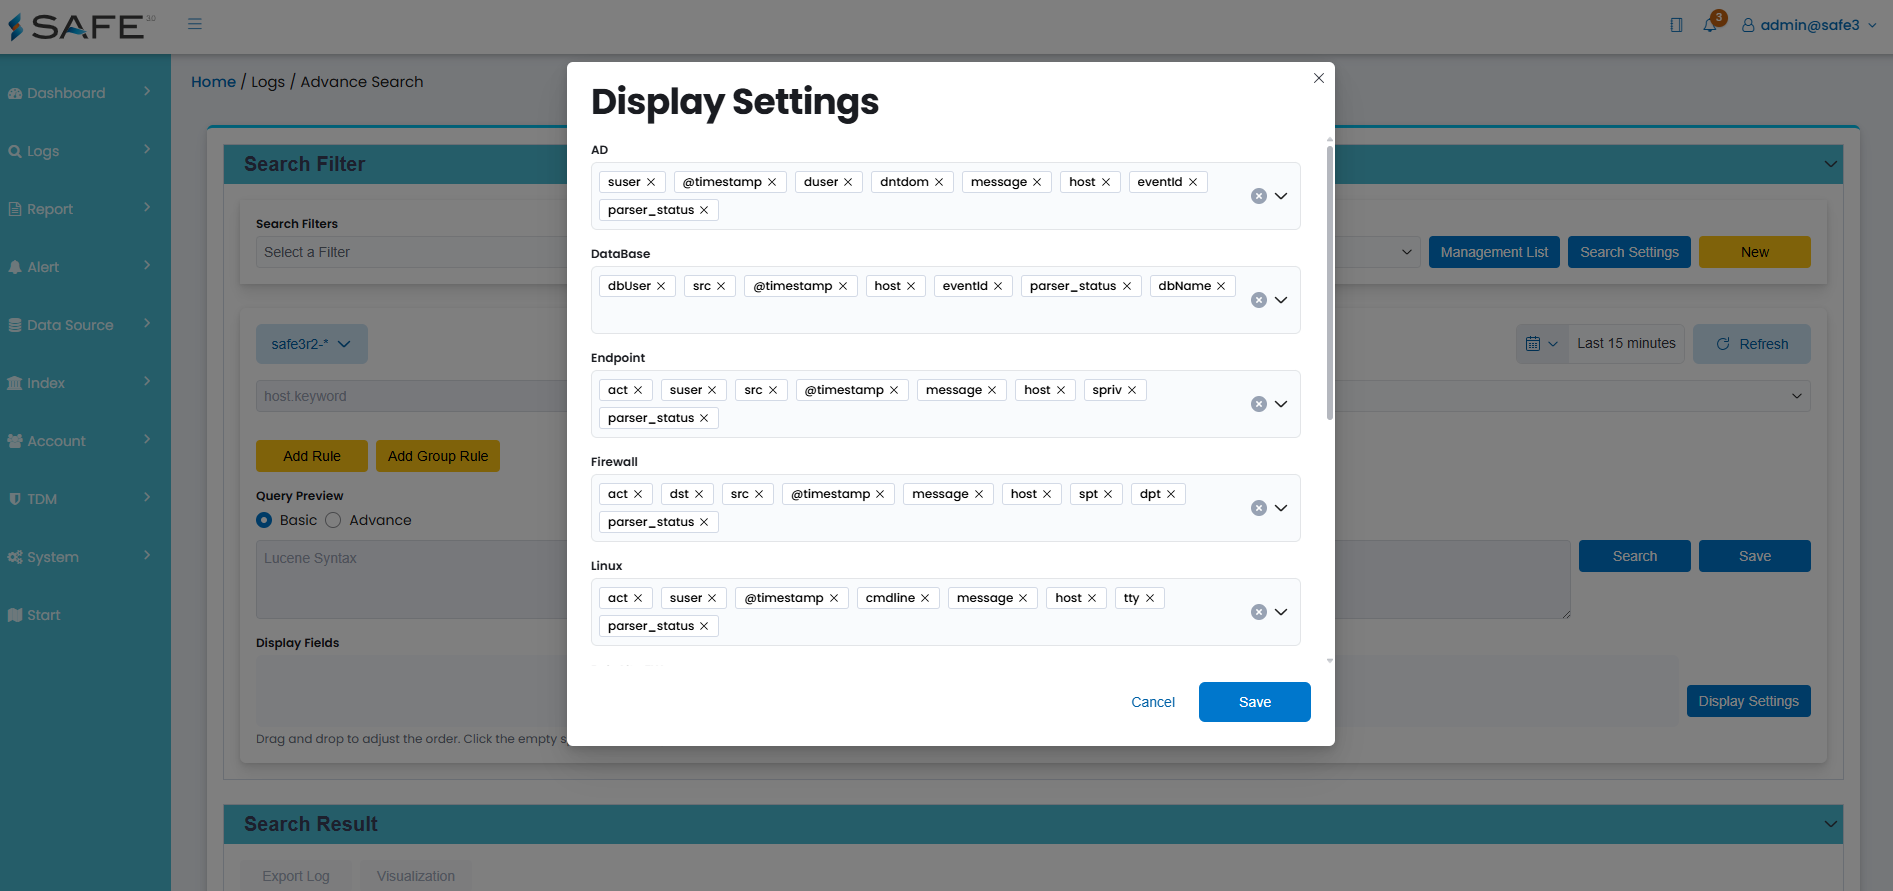
(5) Default Display Field Settings:Click “Display Settings” to open the field configuration page. Users can configure the default log fields to be displayed for each predefined category. Select the desired field name from the dropdown menu to set it as a default display field.
3. Basic Search Feature Introductio
(1) Basic Query
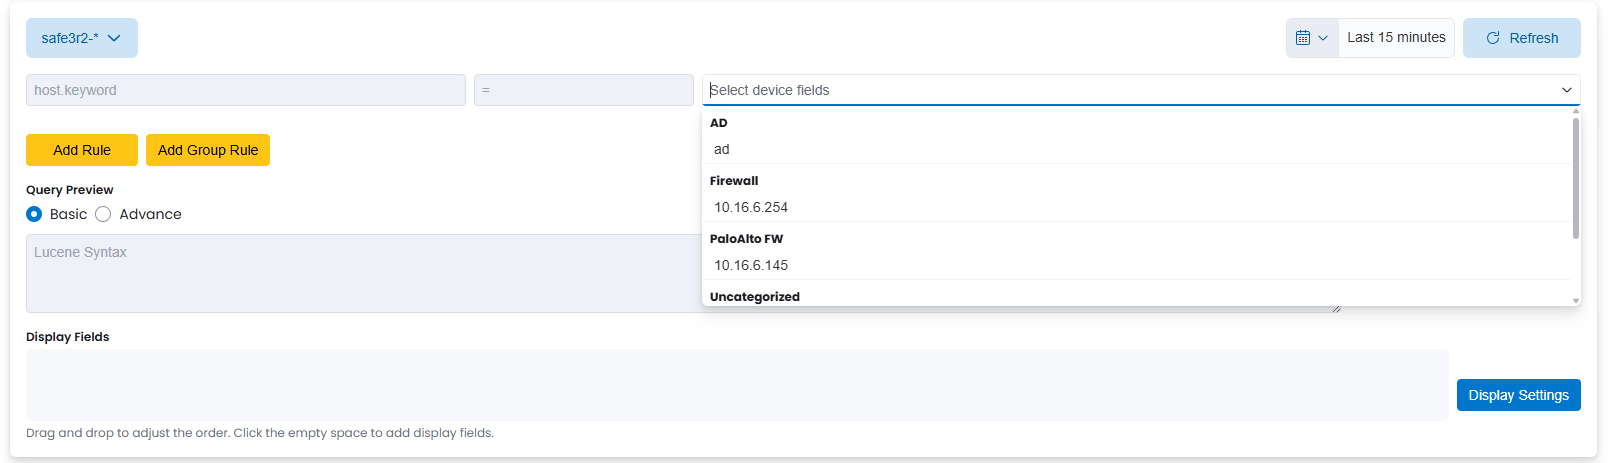
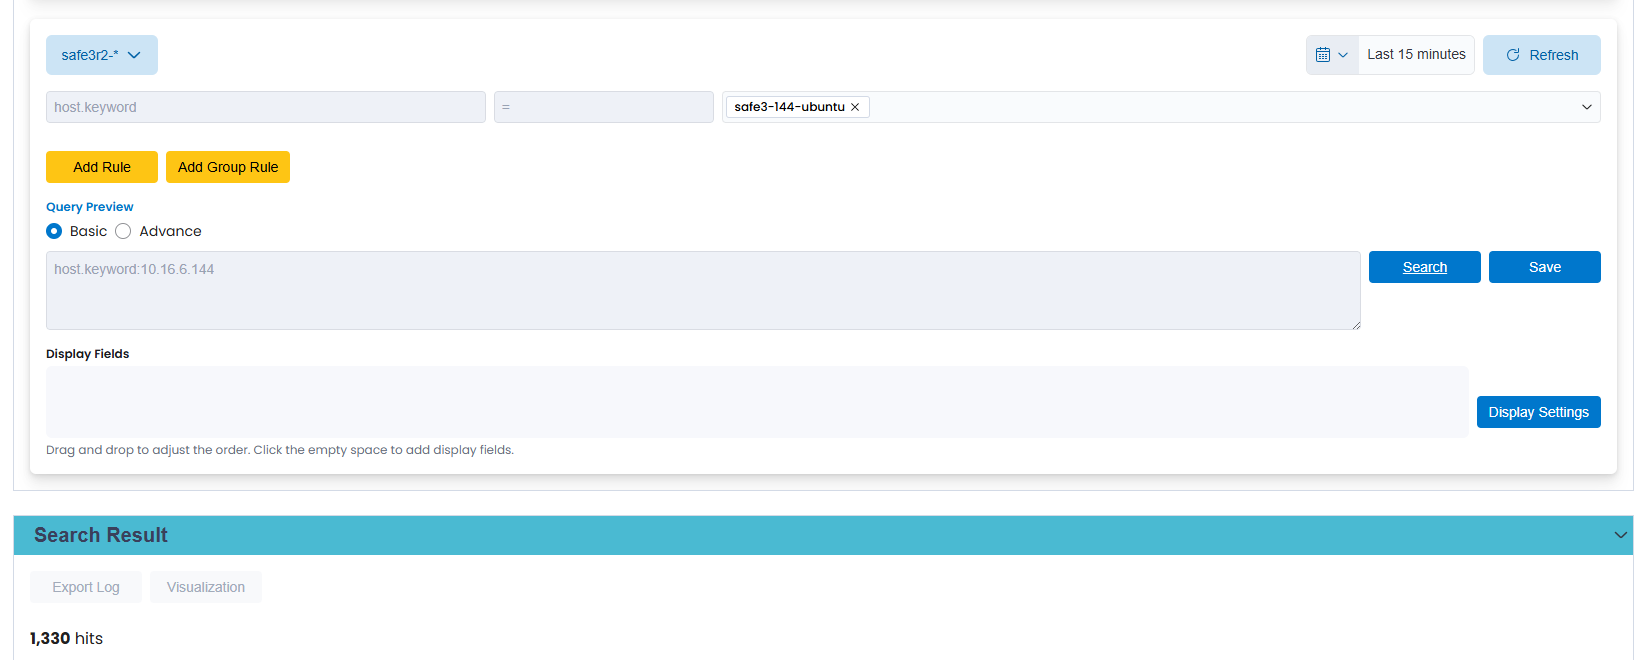
Click to open the dropdown list and select the host whose logs you want to query.
-
After selecting the host, the system will automatically display the default columns.Click Search to display logs that match the specified conditions.
-
Add Display Fields:Click the display field edit box to open the input area and enter the name of the field you want to add.
-
Edit Display Field Order:Drag and drop the fields to rearrange their display order.
-
Delete Display Fields:Click the “x” icon on the right side of a field to remove it.
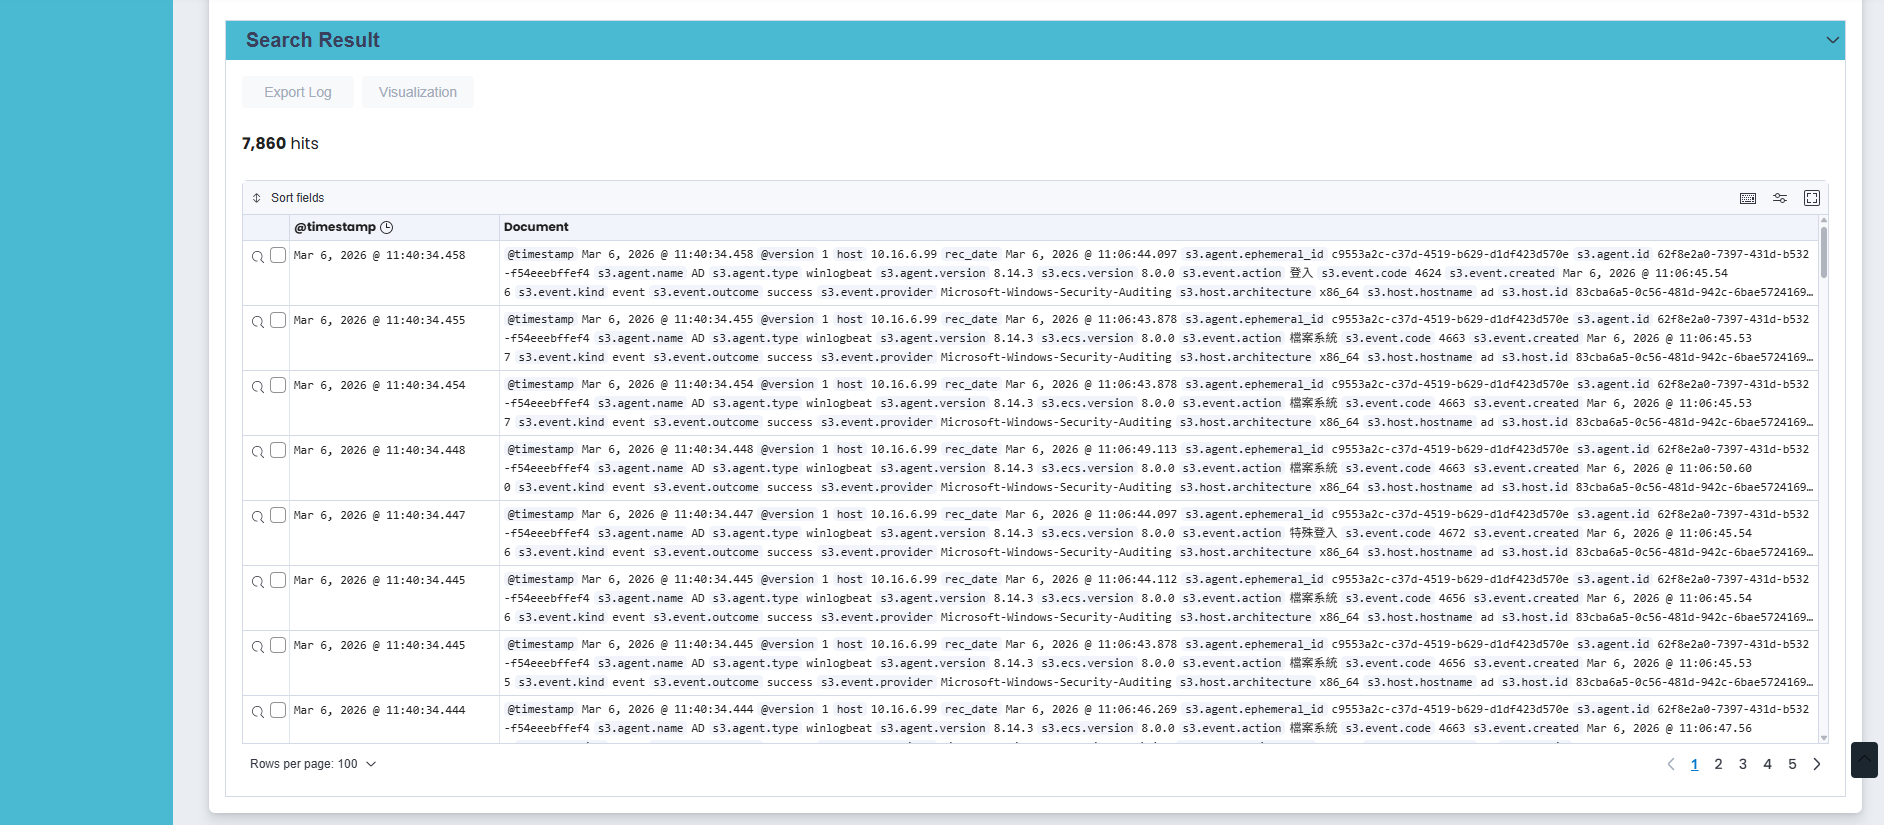
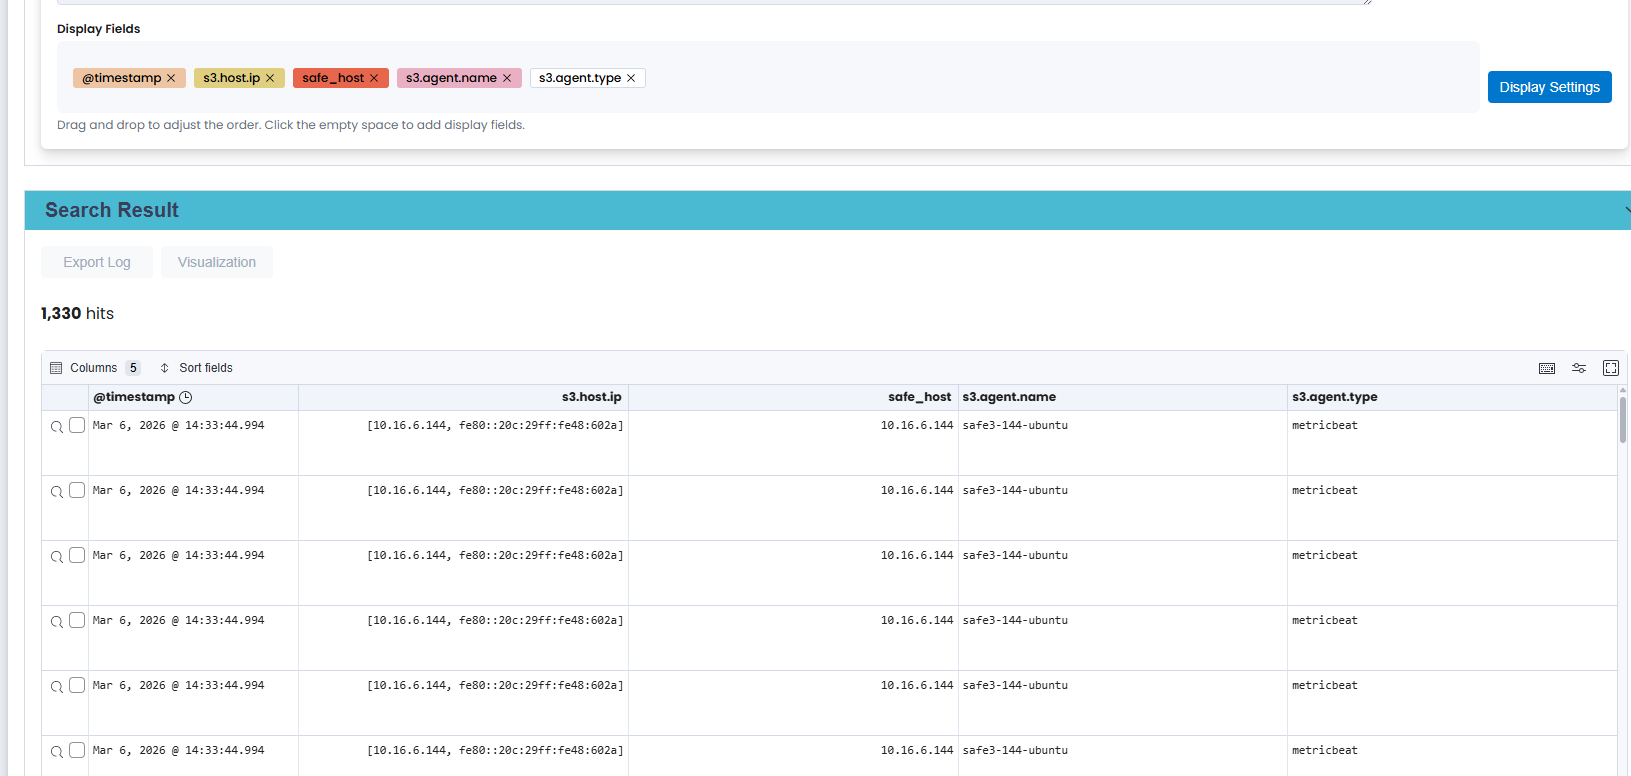
After adjusting the display field names based on the actual log fields, the display result will appear as shown below.
(2) Basic Query Examples
The following examples demonstrate how to perform log searches using multi-level filter conditions.
-
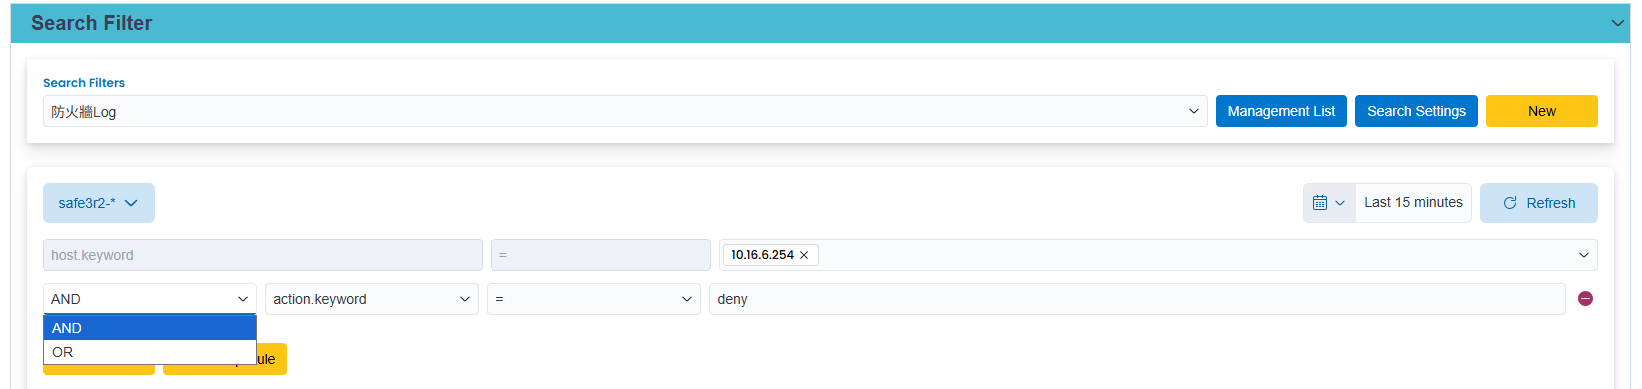
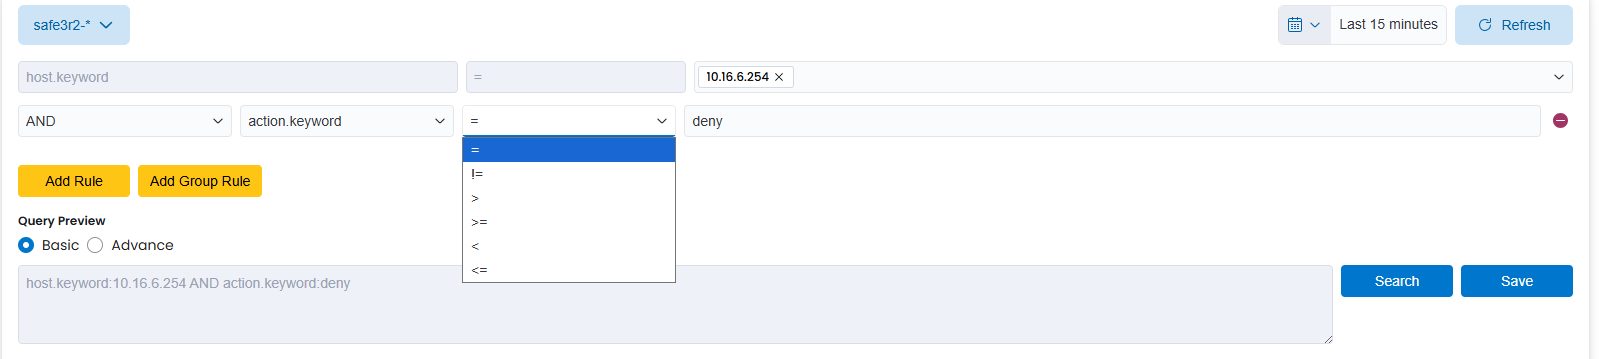
Example 1:Query logs from host IP 10.16.6.254 where action = deny.
- Click “Add Rule” to create a filter condition input field.
- Select AND in the dropdown (AND / OR options available).
- Choose the field action.keyword.
- Select the operator “=”.
- Enter deny in the input field.
- Example 2:Query logs from host IP 10.16.6.254 where action = deny OR action = accept.
- Select host 10.16.6.254.
- Click “Add Group Rule”.
- Set the matching condition to AND.
- Select field action.keyword and enter accept.
- Click “+” to add another rule in the same group.
- Select field action.keyword and enter deny.
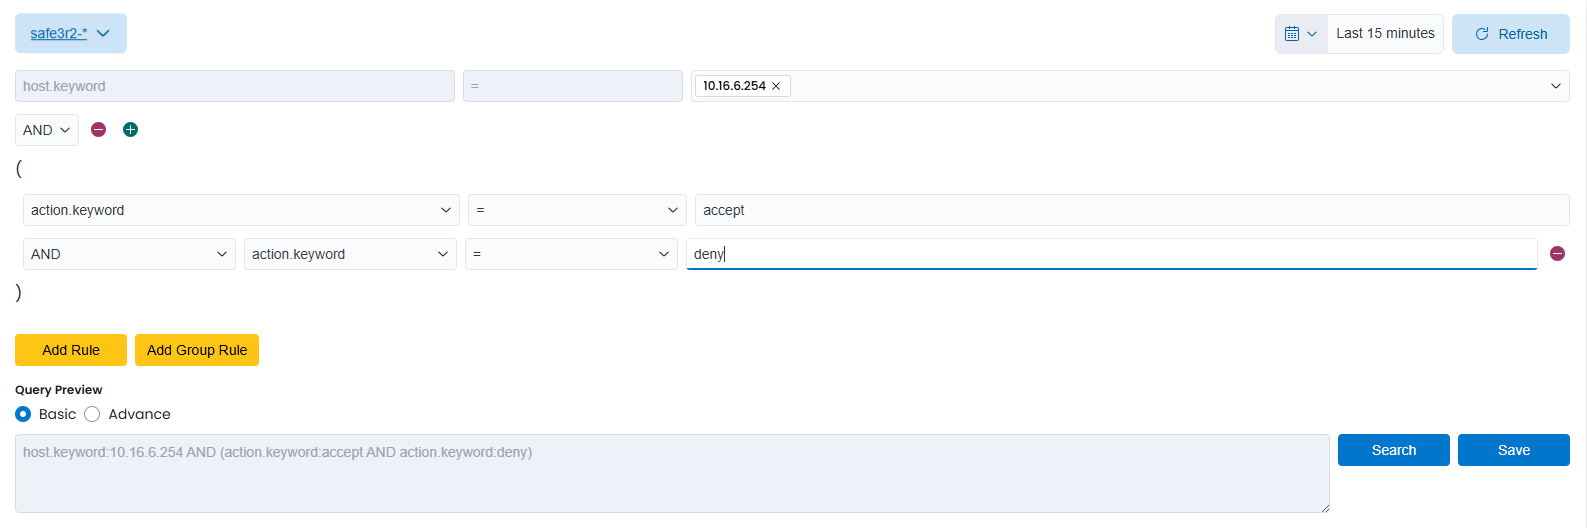
(3) Log Search Results
After setting the filter conditions, click Search.The system will display the matched log entries in the table below according to the configured display fields.
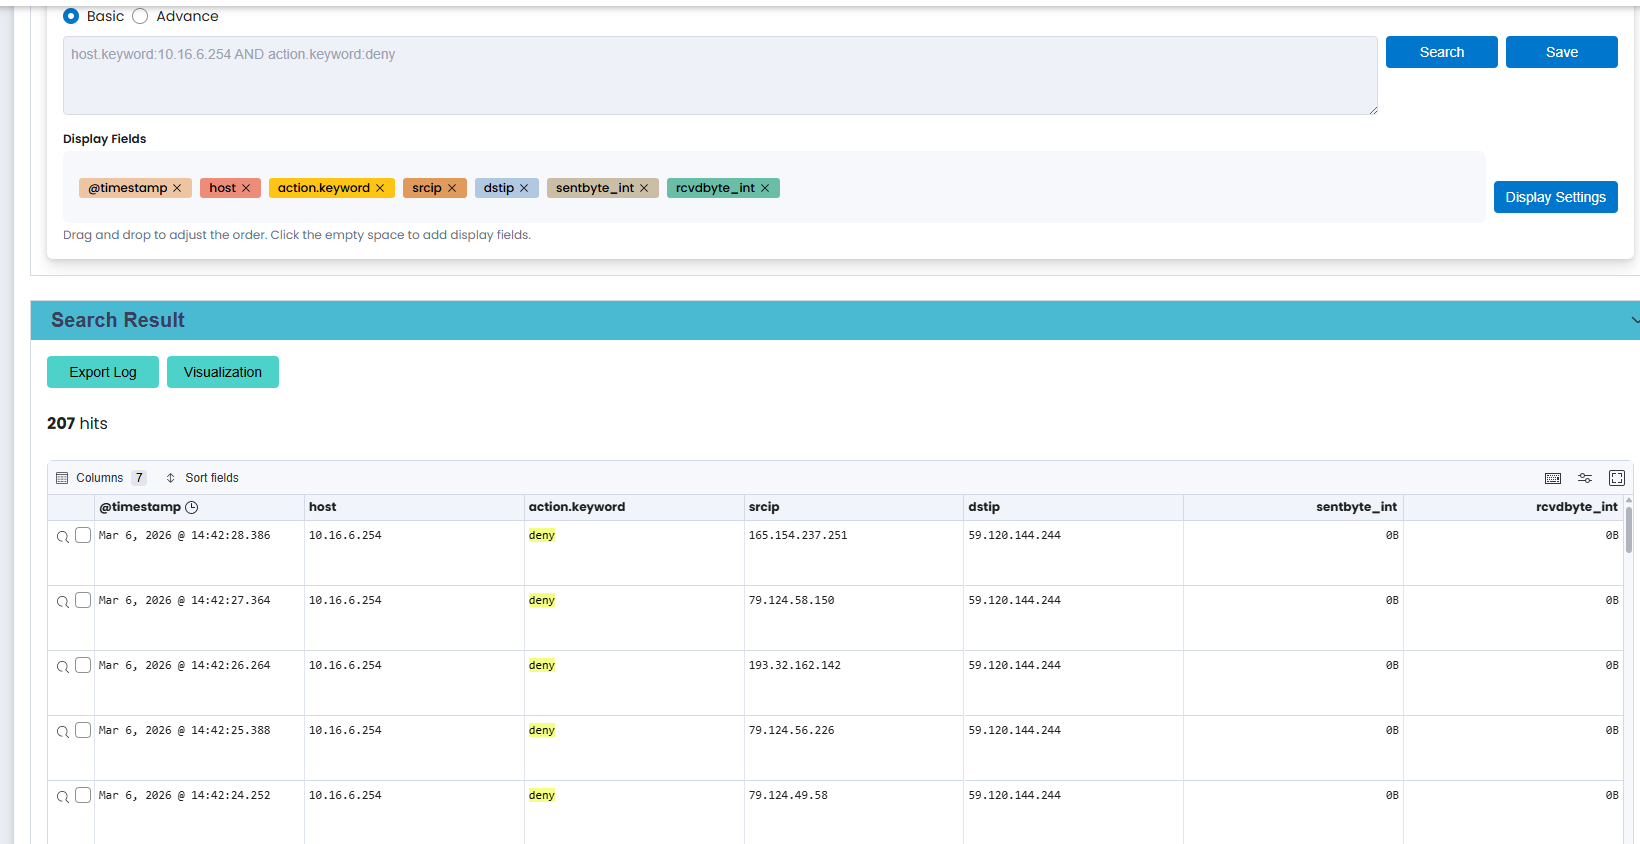
(4) Save Rules
After configuring the search conditions:
-
Click Save.
-
Enter the search condition name.
-
Click Save again to store the rule.

4. Advanced Search Syntax
SAFE3.0 uses Lucene syntax for advanced search queries.The following describes keyword search usage and basic syntax.
- String Query: Consists of one or more words or phrases, with phrases in double quotes, e.g., "test search".
- Specific Field Query: SAFE3.0 supports searching specific fields, e.g., EventID: 4726.
- Regex Query: SAFE3.0 supports wildcards for uncertain strings, e.g., "*" for multiple characters or "?" for a single character.
- Range Query: SAFE3.0 supports range queries, using brackets for inclusive/exclusive bounds, e.g., response time: [10 TO *] for events with response
- time greater than or equal to 10.
- Operators: Use AND, OR, NOT to combine queries, e.g., NOT EventID: 4726 excludes EventID 4726.
5.Keyword Search Example
Query logs from host IP 10.16.6.254 where action = deny OR action = accept event in the past 24 hours:
- Select "Logs" → "Advance Search" from the left sidebar.
- Chooce Advance.
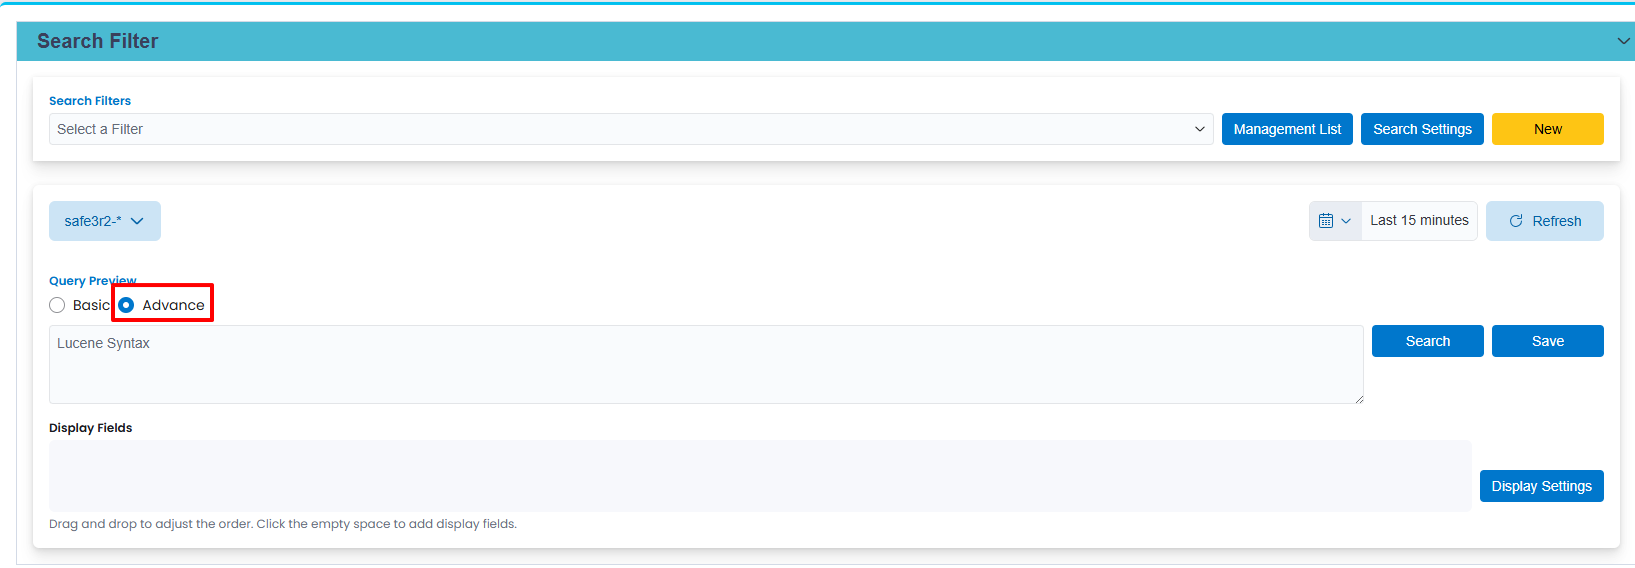
- Choose the log time range (last 24 hours) in the query screen.
- Enter the query string host:10.16.6.254 AND action:(deny OR accpet) in the search field.
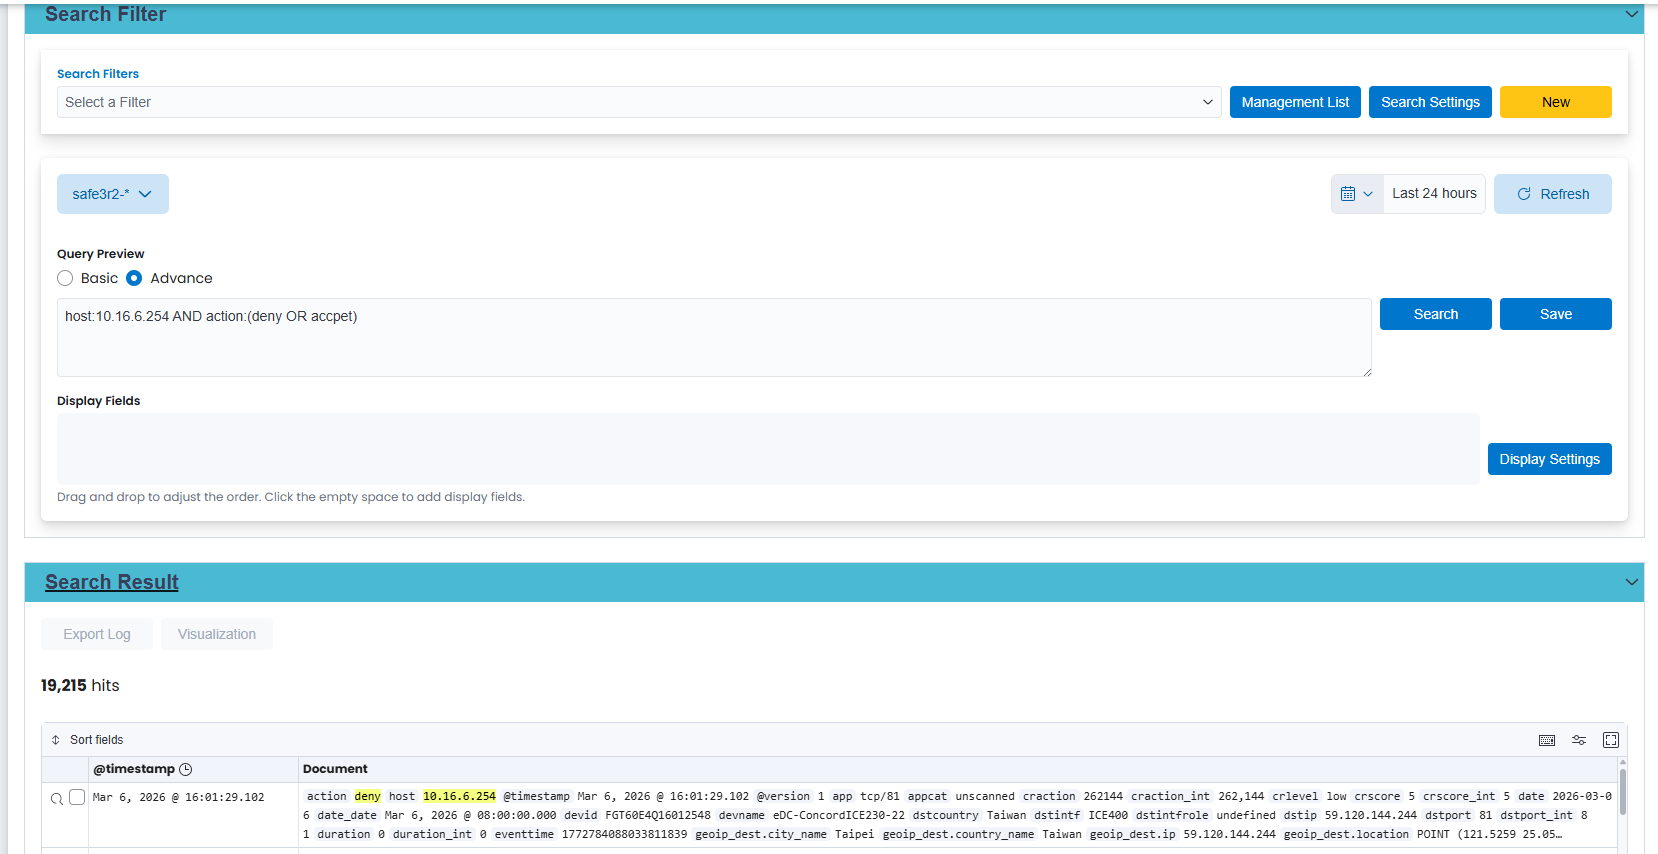
6. Export Logs
- After saving the search conditions, the previously disabled Log Export button will become available.
- Click the button to export logs within the specified time range that match the search conditions.
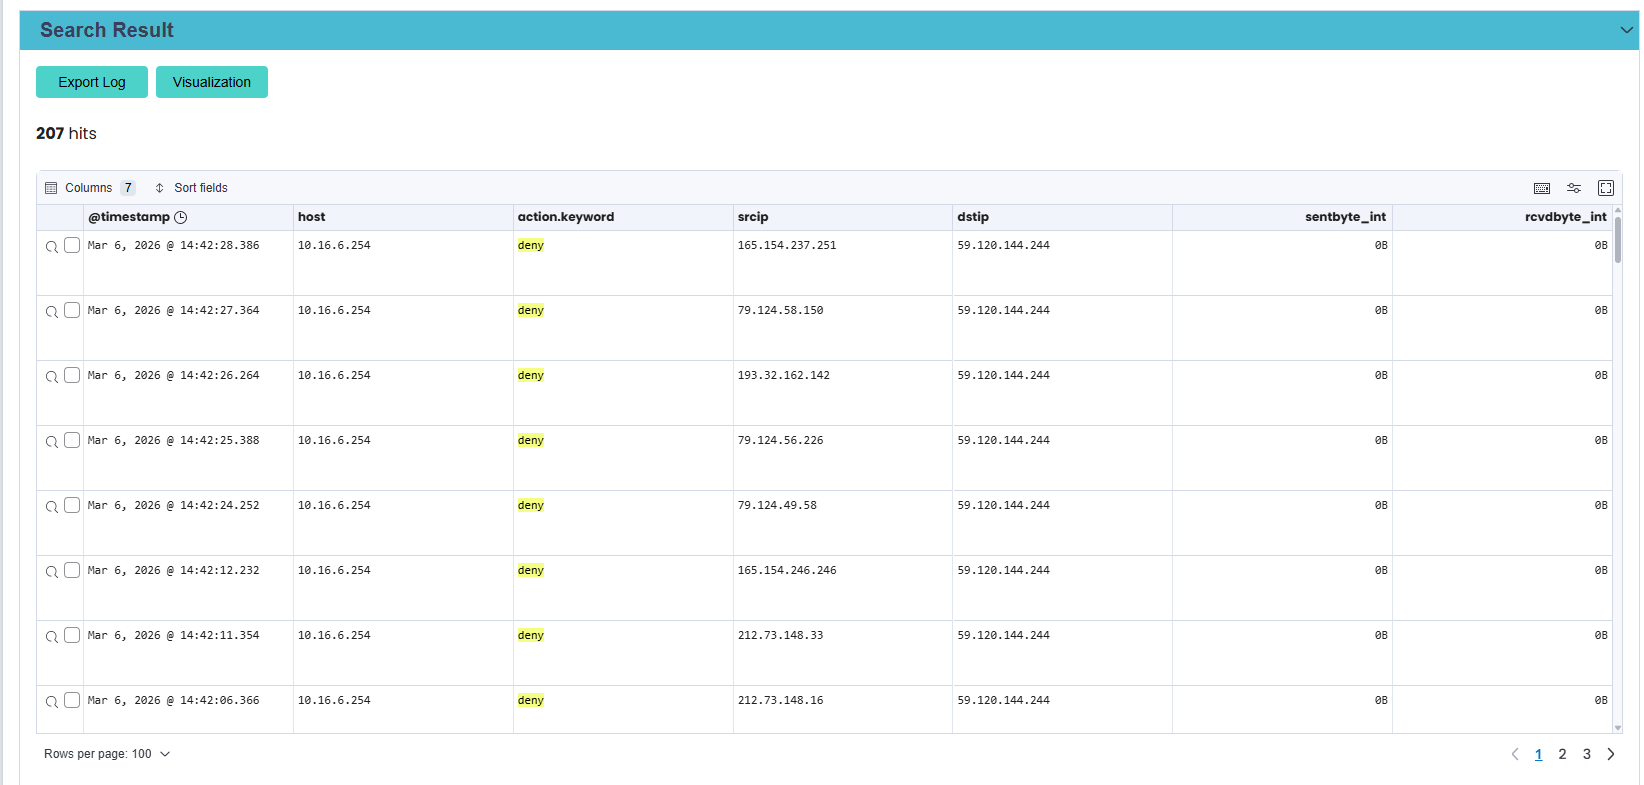
7. Visualization
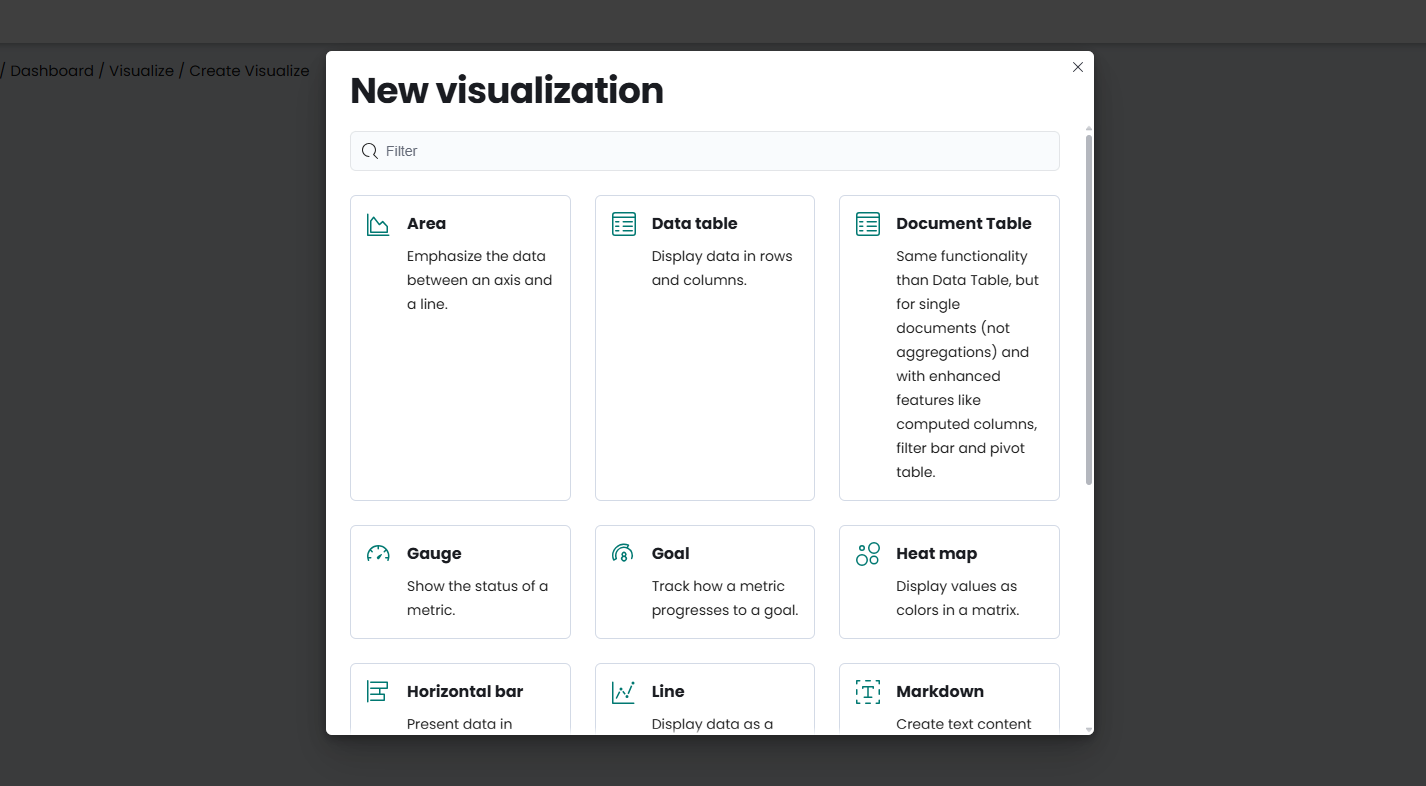
- After saving the search conditions, the Visualization button will become available.
- Click the button to open a new page for creating a visualization component.
- The system will automatically apply the saved search conditions, allowing users to directly create visualizations based on those conditions.
Scheduled Export
From the left menu, click "Logs" → "Scheduled Export" to enter the scheduled export settings page.

1. Add Schedule
Click the add icon to open the schedule settings page.
(1) Filter Name: Click the input box to open the dropdown menu and select the filter condition for scheduled export.

(2) Receiver:Required field. Select the recipient group or enter an email address.
(3) Export Cycle
- Hourly: Data is generated and sent every hour.
- Daily: Data is generated and sent once a day.
(4) Export Time:When set to daily, specify the time of day for data generation.
Click "Save" to complete the settings.
3.2啟用排程

Data Download
(1) Click the download icon to download the logs.

5. To delete log CSV files, check the file’s checkbox and click Delete to complete the deletion.

6. Click the calendar icon to open the scheduled export settings page.